How Do You Check If a PHJOY Link Is Real or a Phishing Copy?
A genuine PHJOY link always runs over 256-bit HTTPS encryption, loads your existing username and exact centavo Peso balance without asking for a new sign-up, and never requests your 4-digit GCash MPIN on the login page. Before tapping any link sent via SMS, Facebook Messenger, or Telegram, run our 4-point domain inspection below so fake lookalike sites cannot steal your password or e-wallet OTP.
- Check the HTTPS Lock & Certificate: Tap the padlock icon in Chrome or Safari to confirm the connection is encrypted and free of browser phishing flags.
- Reject Shortened Bit.ly / TinyURL SMS Links: Scammers hide fake login screens behind URL shorteners sent from unknown 09XX numbers.
- Test With Your Existing Username Only: A real link recognizes your account and VIP tier; a fake clone either steals your login or says "User Not Found."
- Verify the Cashier Redirect Path: Real deposits only ask for your GCash or Maya login on the official payment gateway after you type a ₱100+ amount.
Why Fake "PHJOY Casino Link" Clones Target Filipino Players
Nearly 3,800 searches every month in the Philippines are for "phjoy link" and "phjoy casino link." Fraud rings know that local players frequently switch between mirror URLs when an older address gets blocked on Smart or Globe data, so they buy cheap lookalike domains (with extra hyphens or misspelled letters like phj0y-vip-claim.xyz) and blast them out via bulk SMS.
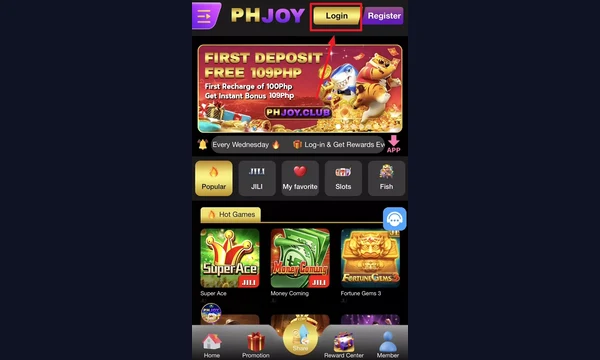
Those fake pages copy the exact purple and gold banners from the real lobby. Their goal is simple: trick you into typing your username and password - or worse, a fake "GCash Account Verification" form - so they can log into your real account and withdraw your Peso balance.
If you receive a text message on your smartphone saying "Congrats! Your account won a ₱888 Free Angpao, click this link and enter your GCash OTP to receive instant cash," delete it immediately. Official promotions are claimed strictly inside the logged-in Rewards Center or Promotions tab - never through an external SMS form.
Here is a street-smart trick our Taguig testing team uses whenever we inspect a new mirror URL: type your real username, but intentionally type a completely fake password (like WrongPass123) on the first try. A real server connected to the database will immediately reject it with "Incorrect password." A dumb phishing form built to steal credentials will accept the fake password and redirect you to a fake "Verify Your GCash MPIN" screen!
Comparing Official PHJOY Entry Channels vs Risky Link Sources
Not all links carry the same risk. Before you bookmark an address on your phone, see how different link sources stacked up during our security checks.
| Link Source | Safety Rating | What You Should Check First |
|---|---|---|
| Installed 7.68 MB Android App | Highest Safety | Connects directly to the active API server without browser URL typing or phishing risk. |
| Verified Bookmark on Your Phone | High Safety | Once you confirm a working HTTPS gateway that shows your exact centavo balance, save it to your browser bookmarks. |
| Facebook Comment / Group Links | High Risk | Often posted by impersonators posing as "Customer Support" or "VIP Agents"; never enter your password via Facebook in-app browser. |
| Random SMS Shortlinks (bit.ly / cutt.ly) | Extreme Risk | Frequently used for credential harvesting and fake APK downloads; never tap or install files from SMS links. |
Why You Should Never Sign In Inside the Facebook or Messenger In-App Browser
Even when a link is 100% real, opening it inside the built-in browser of Facebook Messenger, Viber, or Telegram causes two major headaches for Filipino players:
- Hidden URL Bar & SSL Details: In-app webviews hide the full domain name and SSL certificate details, making it much harder to spot a fake URL.
- Broken GCash & Maya Cashier Callbacks: When you tap Deposit ₱100 inside Messenger's mini-browser and switch to your GCash app to approve the payment, Messenger often closes the mini-browser window in the background - leaving your ₱100 deposit uncredited until support manually matches your 13-digit reference number.
If you ever open a link from a social app, tap the three dots in the top-right corner of the screen and select Open in external browser (Chrome / Safari) before signing in or opening the Peso cashier.
Related Access & Security Guides
Return to our main account sign-in guide for complete login troubleshooting, see how browser DNS fixes work on 1.1.1.1, compare the number 23 backup mirror, or check our independent legit and security audit.
Frequently Asked Questions
How can I tell if a PHJOY link is an official mirror or a fake copy?
Use the wrong-password probe first: enter your username with a deliberately wrong password. An official mirror connected to the real database will reject it immediately, whereas a phishing page will accept anything and ask for your GCash PIN. Once signed in with your real password, confirm your exact centavo balance and bet history.
Why do official casino links in the Philippines change domain extensions?
Local telecom providers (Smart, Globe, DITO, PLDT, and Converge) periodically update network routing and DNS filters, so operators maintain multiple synced mirror domains to ensure players can always access their Peso wallets and pending withdrawals.
Is it safe to download the Android APK from any PHJOY link?
Only download the 7.68 MB Android APK from the official Download tab after you have verified your logged-in account balance. Never install an APK file sent directly as an attachment in Telegram, Messenger, or Viber.